Post by @rqm
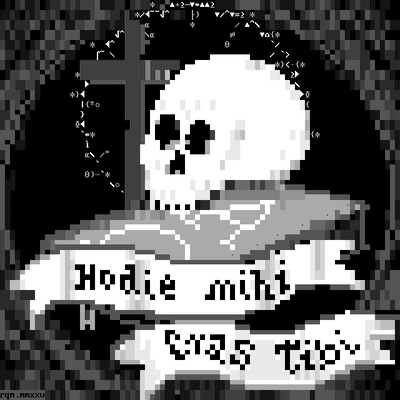
New local kernel exploit for #OpenBSD called #bigfish gets attackers root with KARL/SMAP/SMEP enabled, with building blocks in the chain going back ~37 years to the original BSD sources:
https://calif.io/research/big-fish
It also has really cool ANSI art. 😉
21 likes
 ananas@ananas@scicomm.xyz
 zyxhere💭@zyx@treehouse.systems
 svp@svp@akkoma.mespr.it
 Techokami@techokami@woof.tech
 pat@pat@merveilles.town
 Oblomov@oblomov@snowfan.it
 shellsharks@shellsharks@shellsharks.social
 tbb@tbb@mastodon.social
 Haelwenn /элвэн/
 @lanodan@queer.hacktivis.me
 Bart Coppens@bartcopp@mastodon.social
 MaddieM4@MaddieM4@raphus.social
 Valkyagan@valkyagan@mastodon.social
 DarkCyberman@darkcyberman@nerdculture.de
 Erik L. Midtsveen@midtsveen@mastodon.bsd.cafe
 AT@at@mathstodon.xyz
 Børge@noexec@bsd.cafe
 Jendys@jendys@witter.cz
 Johannes Brakensiek@lazarus@fosstodon.org
 Martin Schröder 🇺🇳@oneiros@ruhr.social
 Danielle@d@greennuclear.online
 Stefano Marinelli@stefano@bsd.cafe
17 boosts
svp@svp@akkoma.mespr.it
Mudb0y@Mudb0y@universeodon.com
Techokami@techokami@woof.tech
Oblomov@oblomov@snowfan.it
 Laurent Bercot@ska@treehouse.systems
MaddieM4@MaddieM4@raphus.social
DarkCyberman@darkcyberman@nerdculture.de
 troubledwater@troubledwater@social.tchncs.de
Erik L. Midtsveen@midtsveen@mastodon.bsd.cafe
Valkyagan@valkyagan@mastodon.social
Jendys@jendys@witter.cz
Johannes Brakensiek@lazarus@fosstodon.org
 olok@ol0ck@hackerspace.pl
Martin Schröder 🇺🇳@oneiros@ruhr.social
Danielle@d@greennuclear.online
 Tomáš@prahou@merveilles.town
Stefano Marinelli@stefano@bsd.cafe
@rqm The first mitigation that comes to mind is that of Capsicum where the capability to invoke shmat() is never granted. Only the mapping of POSIX anonymous shm segments is permitted. Granted, that is FreeBSD specific, but it points towards the incompleteness of the pledge model in OpenBSD. In-kernel mitigation is most likely only possible with PAC/MTE on arm64 or PKS on x86-64 which is neither supported nor adopted.
@rqm Pretty impressive!
I am looking forward to getting this patched on all of my servers, but for my hosts I am hoping for 8.0 as it resolves some issues for me.
I do have direct SSH access on hosts, but it's under a very restricted shell and I'm not sure you can spin up enough processes to pull it off.
```
vmuser:\
:umask=022:\
:datasize=16M:\
:coredumpsize=1024:\
:openfiles=20:\
:maxproc=10:\
:tc=auth-defaults:
```